
IntelMCP
Threat intelligence from public Telegram channels, searchable and monitored inside Claude.
 View in the Claude registry
- Brand
- IntelMCP
- Category
- Security
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
Integration details
Description
IntelMCP gives Claude access to messages collected continuously from curated public Telegram channels about threat actors, ransomware, hacktivism, data leaks, vulnerabilities and IT/OT security, with edits, forwards and extracted indicators (IP addresses, domains, URLs, file hashes, CVE identifiers and countries). Coverage is deepest for the Middle East and the Gulf, Iran–Israel, Russia–Ukraine hacktivism, and leak, ransomware and CVE trackers. Security analysts use it to: - search the last 90 days of collected messages in their original languages, including Arabic, Persian, Russian and Hebrew; - look up an indicator and see every post that mentions it; - trace a claim to its earliest copy in the collection through forwards and copies; - set up alert rules (words, patterns or indicators) that match new messages as they arrive, tested against history before saving; - review matches with reposts of one event grouped into a single incident, record verdicts, and send matches to a signed webhook. A built-in setup prompt asks the analyst two questions (what to watch for, and which regions), drafts starter rules and tests them against recent history, then shows one summary with each rule's expected alerts per day. On one approval it creates the rules and watch profile, matches the last 7 days of history, and shows the newest matches with an offer to judge them. Run again when monitoring exists, it tunes the existing rules and profile instead of creating new ones. A triage prompt judges unreviewed matches a page at a time against the watch profile and summarizes the relevant ones by severity. A dashboard prompt gives a visual overview of the monitoring, and an investigate prompt researches a question across the collection with every point cited. All analysis runs in the user's own Claude; IntelMCP only stores and searches the collection and the user's own settings.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
- Secondary Subcategories
- None listed
- Brand
- IntelMCP
- Access
- Account required
- First tracked
- 2026-10-03
- Tool count
- 23
- Geography
- US
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
 Agent DiscoverabilityClaude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
No spam. Unsubscribe any time.
What discovery looks like
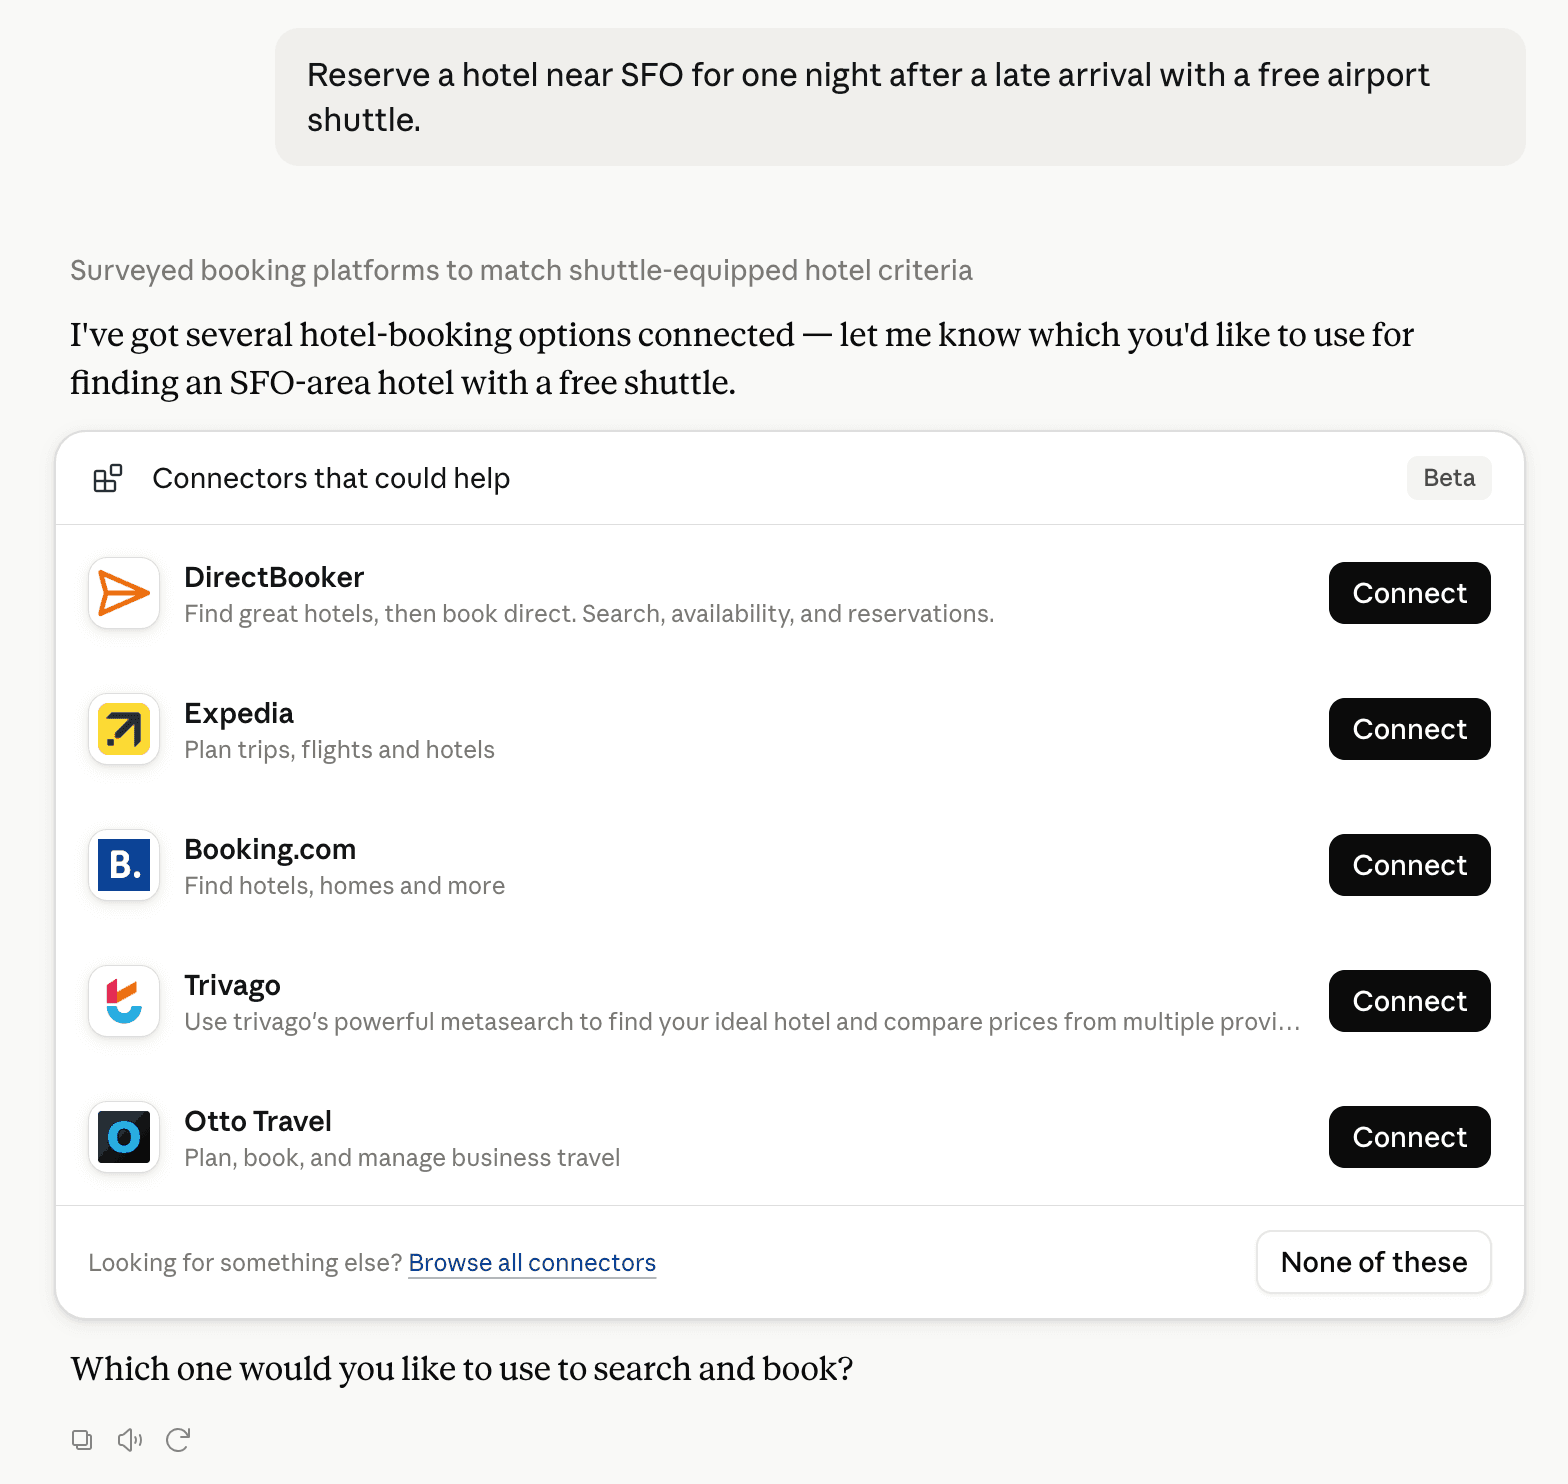
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Threat Detection & SIEM/XDR Monitoring
View Category23 tools agents can invoke

IntelMCP Claude Connector FAQ
How the directory, categories and Discoverability Score work.
Read the methodologyHow do I improve IntelMCP's Claude Connector discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are IntelMCP alternatives on Claude?
As of 2026-10-05, IntelMCP competes with Anvilogic, Brandefense MCP, ELLIO, Exaforce, Fingerprint, Have I Been Squatted, LimaCharlie, SEON and 3 more in Claude Threat Detection & SIEM/XDR Monitoring, ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.