Ansvar AI
Gap analyses, DPIAs, threat models and TARAs across NIS2, DORA, GDPR, the EU AI Act and CRA — every claim cited to verified law, licensed ISO clauses and live CVE data. EU-hosted, free to start.
- Category
- Security
- Primary Subcategory
- Security & Compliance Posture Automation (GRC)
 View in the Claude registry
Integration details
Description
Run regulated security and privacy work inside Claude, with every claim traced to a source you can show an auditor. Ansvar answers questions on NIS2, DORA, GDPR, the EU AI Act, the Cyber Resilience Act (CRA) and national transpositions such as Sweden's Cybersäkerhetslagen, then runs the work built on them: gap analysis, DPIA, FRIA, LINDDUN privacy threat modelling, STRIDE threat models, and automotive TARA under ISO/SAE 21434 and UNECE R155/R156. Ask things like: "Does NIS2 apply to a 60-person SaaS provider in Sweden?" "Compare incident-reporting deadlines under DORA and NIS2." "Map our ISO 27001 controls to CRA vulnerability-handling obligations." "Is this citation still in force?" "What changed in German cybersecurity law this quarter?" "Draft a DPIA for our new HR analytics tool." "Score this CVE for an internet-facing system that can't be patched yet." Vulnerability intelligence is built in: CVE lookup, CVSS environmental scoring, EPSS, CISA KEV status, public exploit references, and VEX export. Coverage: 46 licensing-audited jurisdictions, 262 security frameworks, 5.7M citable legal provisions, court decisions and regulator guidance — plus licensed clause text for ISO/IEC 27001, 27002, 27005, 42001 and ISO/SAE 21434 through SIS (Swedish Institute for Standards). Nothing is scraped. Upload your own policies, contracts or tenders and get paragraph-level, hash-anchored citations that stay provable months later. Where no verified source exists, Ansvar marks the gap instead of papering over it. Grounded, not generated. Built for Legal professionals, CISOs, DPOs, GRC teams, security architects and consultants who need answers they can defend. EU-hosted core. OAuth 2.1. Nothing you send trains anyone's model. Free to start, no card required.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Primary Subcategory
- Security & Compliance Posture Automation (GRC)
- Secondary Subcategories
- None listed
- Brand
- Ansvar AI
- Access
- Account required
- First tracked
- 2026-07-17
- Tool count
- 61
- Geography
- US
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
Claude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
No spam. Unsubscribe any time.
What discovery looks like
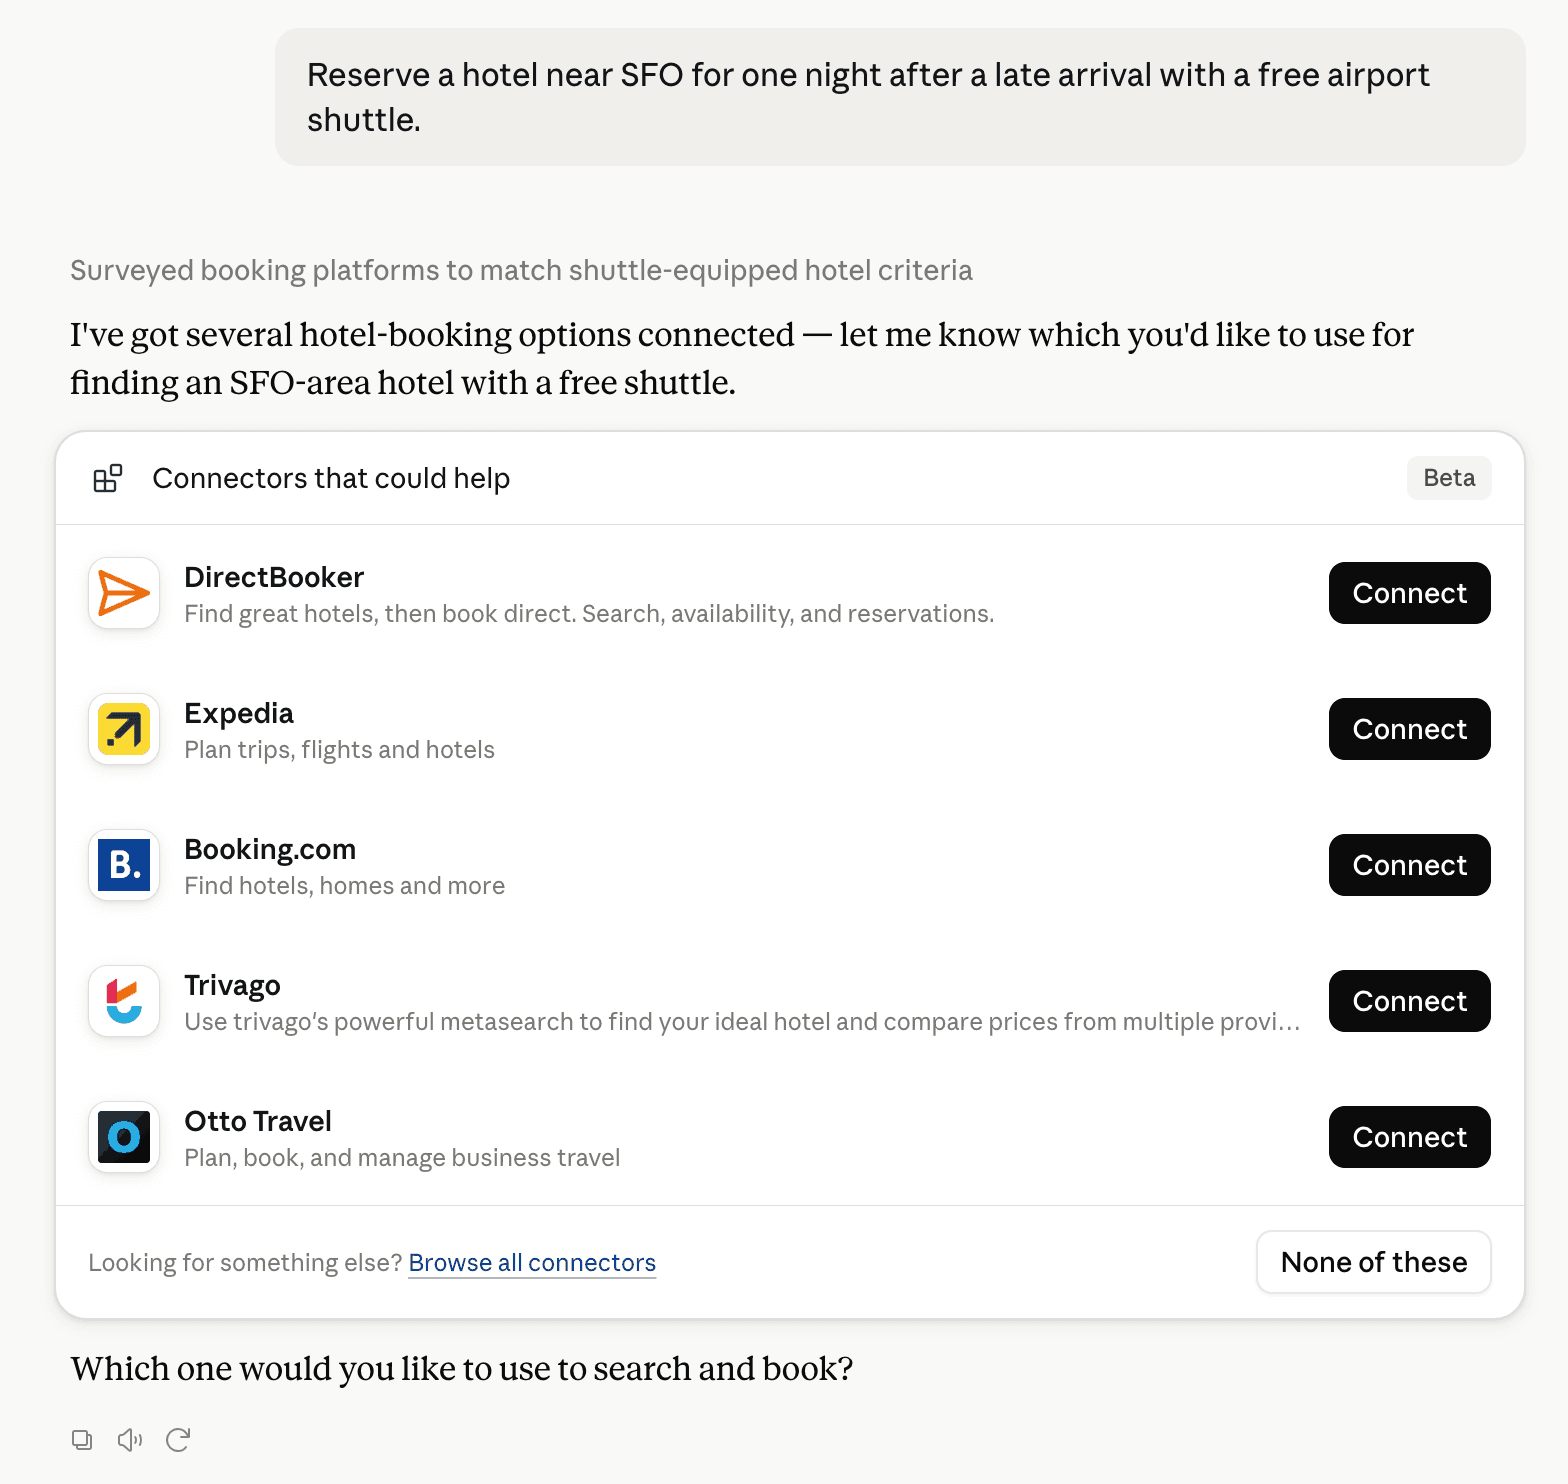
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Security & Compliance Posture Automation (GRC)
View Category61 tools agents can invoke
How do I improve a Community connector's discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are Ansvar AI alternatives on Claude?
As of 2026-09-29, Ansvar AI competes with Sprinto MCP, Pi Security, Drata, Reco, Vanta, Phished, accessibilitytracker.com, Anomity, Assuric, CertScore.ai, CISO360AI, CISOGenie, Decionis Execution Authority, Dtwo, FortMesa, mcp.secureframe.com, Norrsent - Agentic Risk Management & GRC, SAMMY, Sola Security, VComply in Claude Security & Compliance Posture Automation (GRC), ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.