
ORCAPOT
Read-only access to your ORCAPOT honeypot data: attacks, attacker IPs, ML threat scores, campaigns and IOC feeds.
 View in the Claude registry
- Brand
- ORCAPOT
- Category
- Security
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
Integration details
Description
ORCAPOT is a deception (honeypot) platform by Febrics. Organisations deploy decoys (website clones, embedded decoys, marketplace app decoys, custom pages and mail pots), and ORCAPOT records every request that reaches them, scores attacker IPs with machine learning and groups IPs that behave alike into campaigns. This connector gives Claude read-only access to your own organisation's ORCAPOT data, so you can ask in plain language instead of building dashboard queries: - What hit our decoys last night, and which source IPs are the most dangerous? - Did this IP touch any of our decoys, and what exactly did it send? - Which usernames were tried on our decoy login pages? - Are there new or unknown attack patterns (possible 0-days)? - Give me a block list of high-confidence malicious IPs for our firewall or SIEM. - Is someone cloning our website for phishing? 25 read-only tools cover decoy configuration, dashboards, grouped counts, attacker tables, raw requests, IP profiles, ML threat scores, campaigns, emerging threats, AI action recommendations, credential attempts, uploaded files, mail pots, phishing clone findings, daily reports, organisation settings and the IOC / TAXII feed. Built for security teams: - Each connection is bound to exactly one ORCAPOT organisation; you only ever see your own data. - All tools are read-only; the connector changes nothing in ORCAPOT. - Text written by attackers is returned separately as attacker-supplied data, sanitised, with links defanged. - Captured passwords and your team's e-mail addresses stay masked unless an administrator explicitly allows sensitive data. - You choose how long access lasts when you connect and can revoke it at any time in ORCAPOT. Requires an ORCAPOT account with the Read Only or Manager role in an organisation with an active licence.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
- Secondary Subcategories
- None listed
- Brand
- ORCAPOT
- Access
- Account required
- First tracked
- 2026-10-21
- Tool count
- 25
- Geography
- US
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
 Agent DiscoverabilityClaude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
What discovery looks like
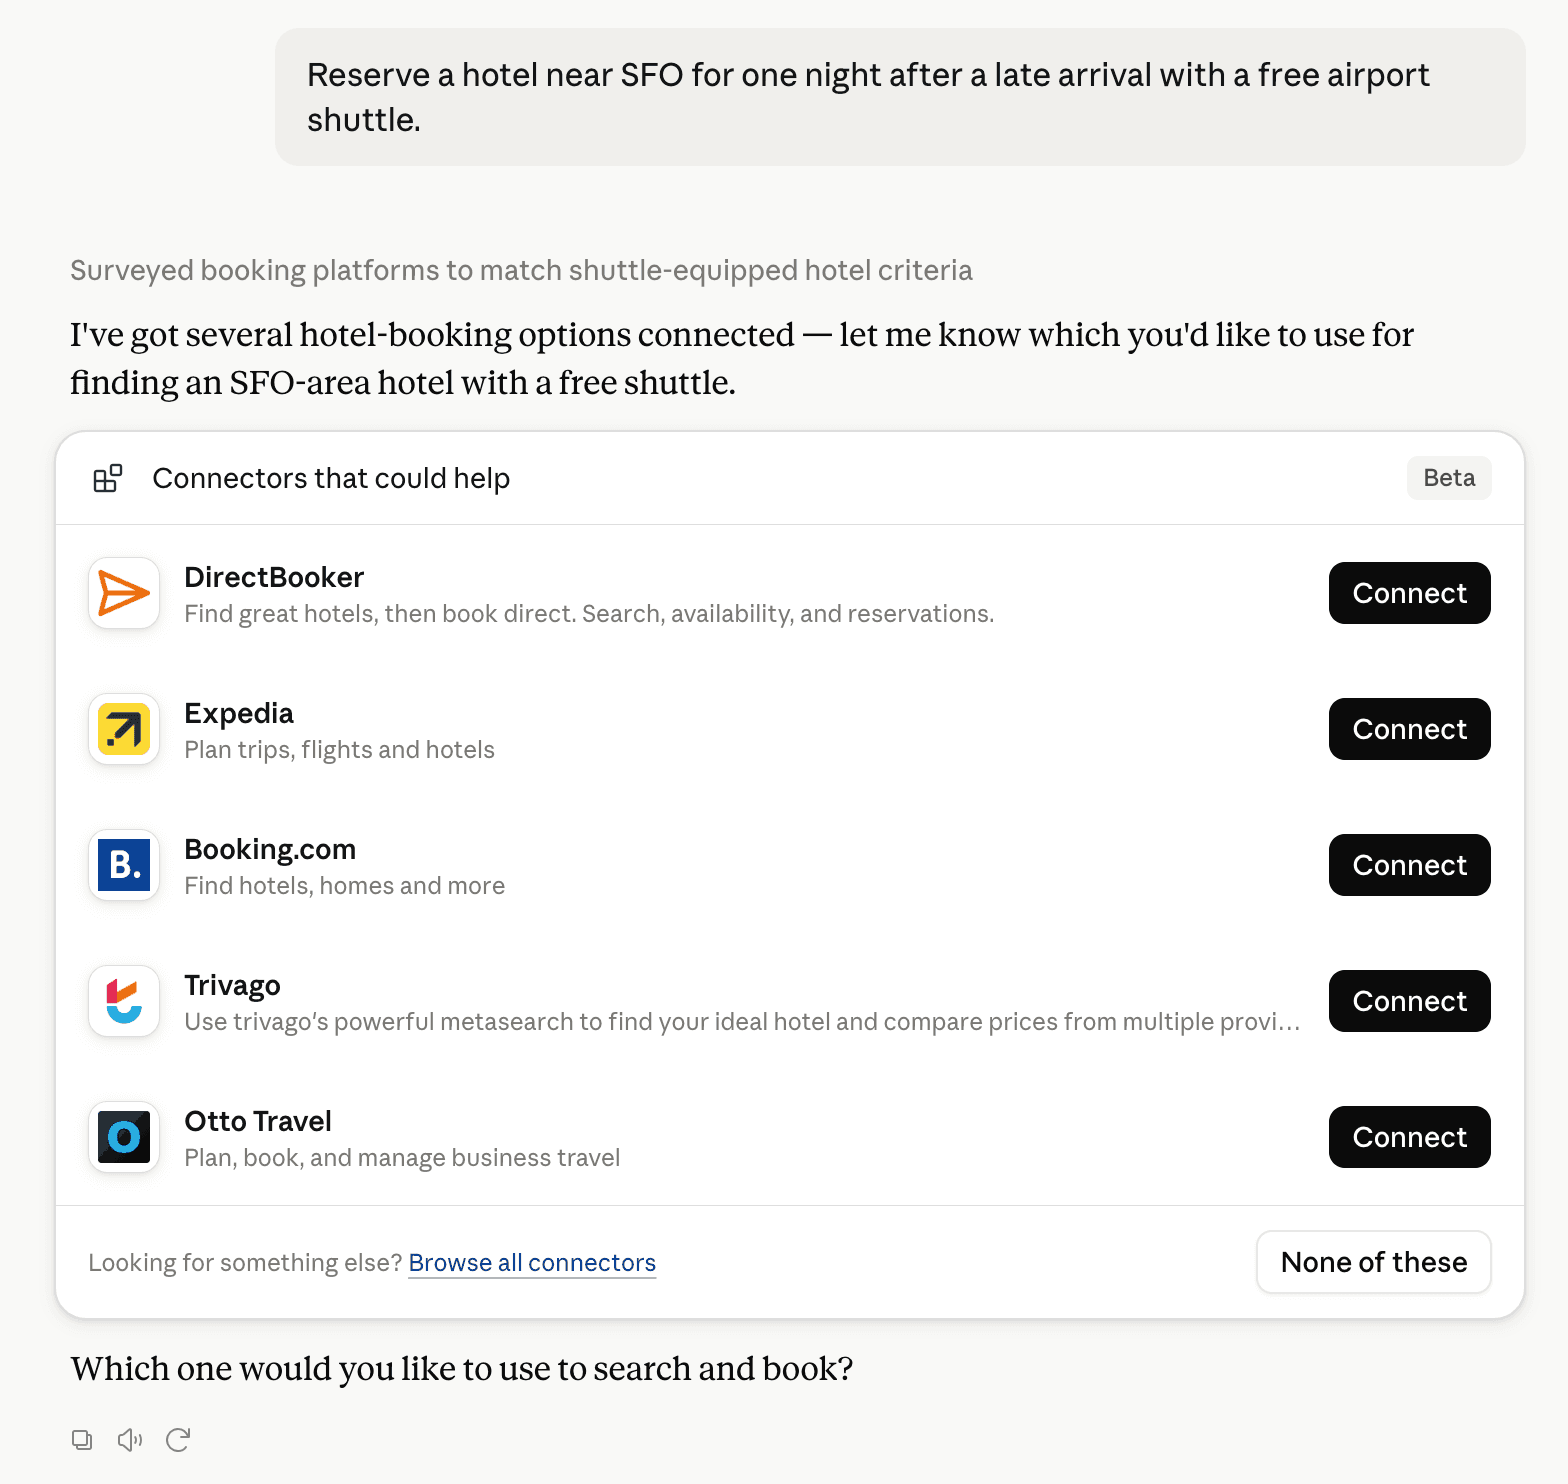
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Threat Detection & SIEM/XDR Monitoring
View Category25 tools agents can invoke

ORCAPOT Claude Connector FAQ
How the directory, categories and Discoverability Score work.
Read the methodologyHow do I improve ORCAPOT's Claude Connector discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are ORCAPOT alternatives on Claude?
As of 2026-10-23, ORCAPOT competes with Anvilogic, Brandefense MCP, DarkWebSonar, ELLIO, Exaforce, Fingerprint, Have I Been Squatted, IntelMCP and 6 more in Claude Threat Detection & SIEM/XDR Monitoring, ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.