
DugganUSA Threat Intelligence
A read-only second opinion for your agent: check packages before install, look up indicators, prioritize patches from CISA KEV, and price AI usage. No key needed; every answer cites its source.
 View in the Claude registry
- Brand
- DugganUSA
- Category
- Security
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
Integration details
Description
DugganUSA is a threat-intelligence corpus of about 29 million records, built from public feeds such as abuse.ch, Spamhaus, OSV and CISA, from published research credited by name, and from our own GitHub hunting and edge sensors. This connector gives Claude read-only access to it. It writes nothing, needs no account, and sits beside the security tools you already use. What you can ask: - Before an install: is this npm, PyPI or RubyGems package, or this GitHub Action, on a malicious-package deny-list or under a published advisory? Answers allow, review or block, with the reason and the record it rests on. - During triage: what do we know about this IP, domain, URL or file hash? Which actor, which campaign, which feeds, and how confident? - When patching: where does confirmed exploitation concentrate for this vendor, and is the risk chronic or new? - For research: search across threat actors, campaigns, CVEs and 1,800+ research posts in plain language. - For FinOps: what does this model or this agent session cost at list price? Rates are dated and copied from each provider's own pricing page. Who it is for: AI agent builders who want a pre-install check, security teams triaging alerts, neocloud and GPU-infrastructure operators watching the AI serving stack (inference caches, model servers, theft of metered inference capacity), and anyone who has to put a dollar figure on AI usage. Absence is not proof of safety: when we hold no record, the tool says so rather than calling it clean. Corrections are published in public at dugganusa.com.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
- Secondary Subcategories
- None listed
- Brand
- DugganUSA
- Access
- No account required
- First tracked
- 2026-10-23
- Tool count
- 7
- Geography
- US
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
 Agent DiscoverabilityClaude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
What discovery looks like
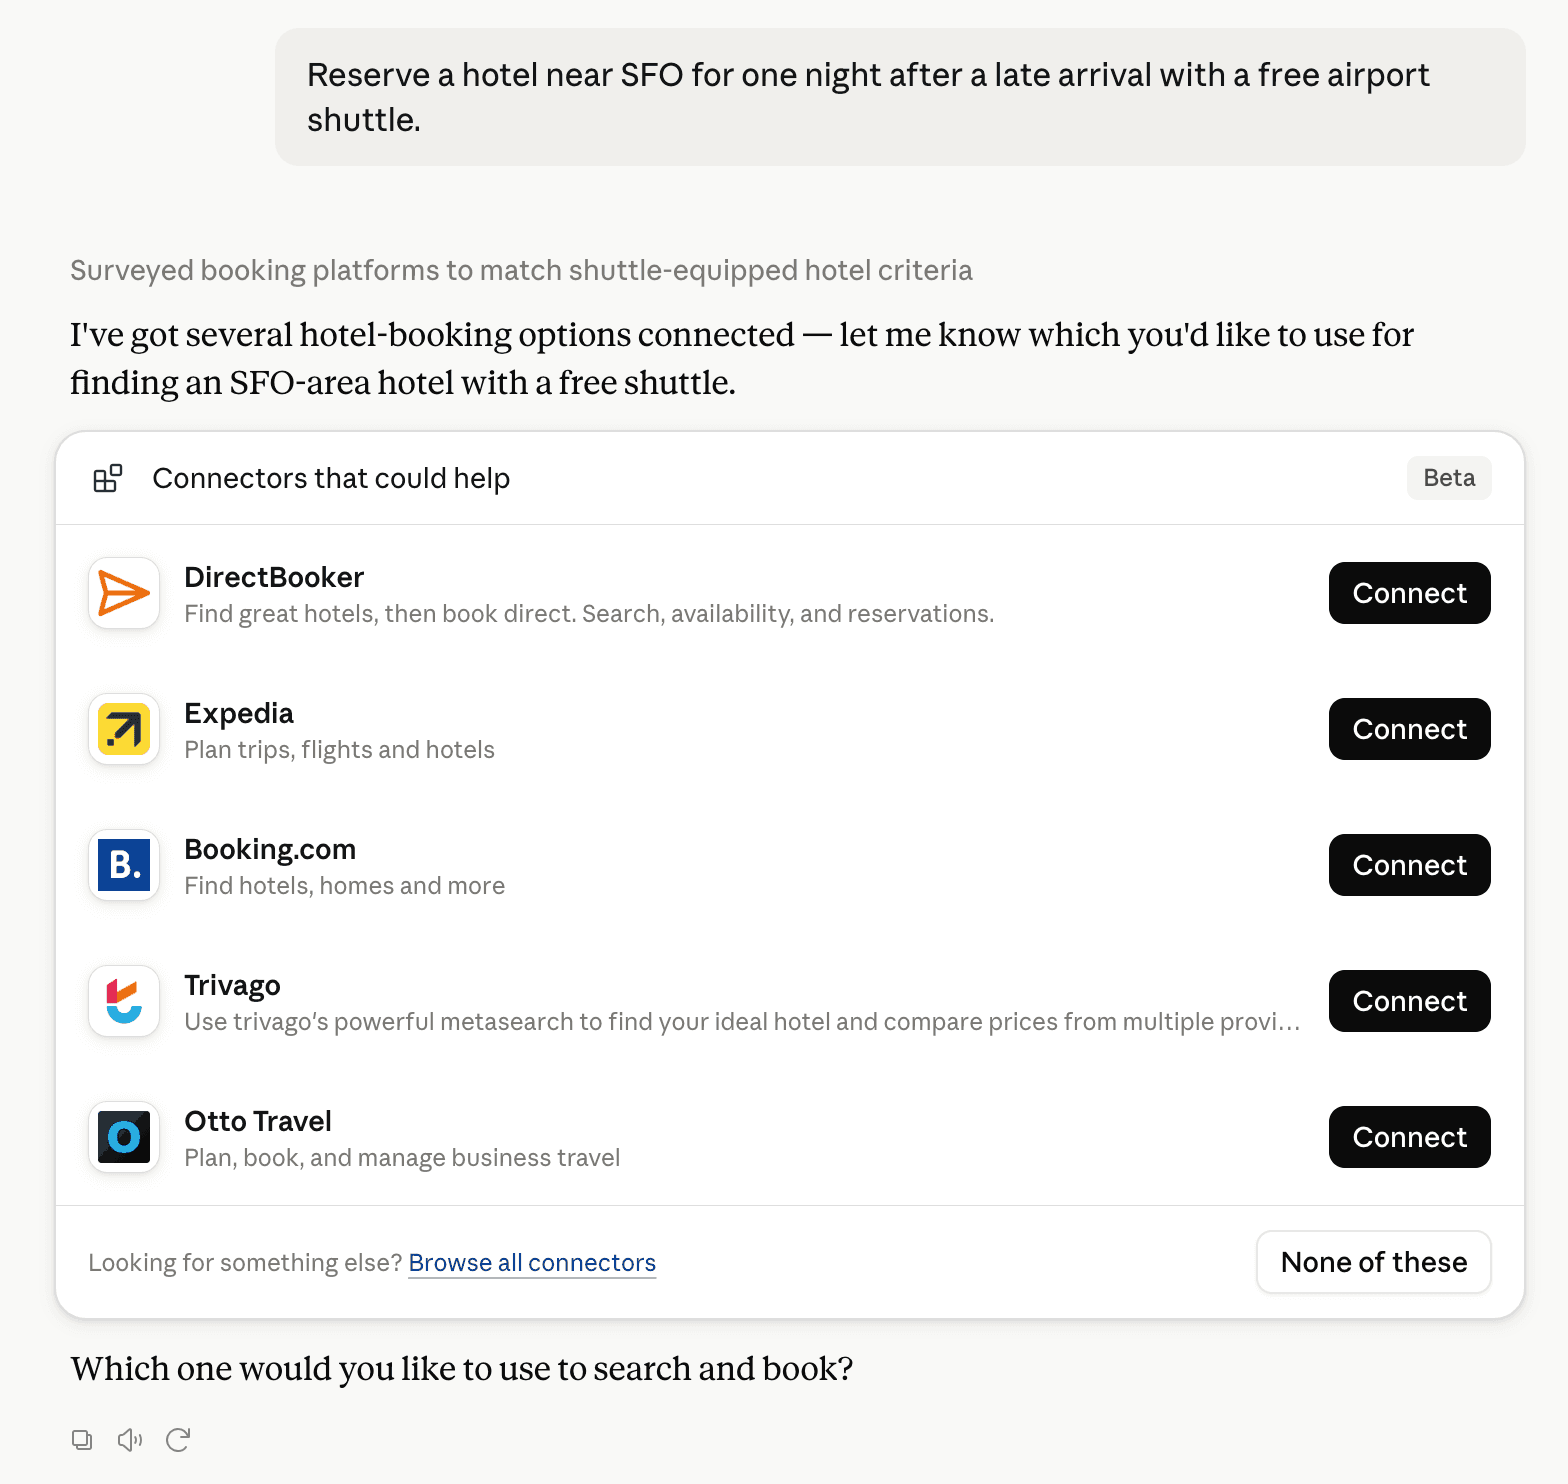
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Threat Detection & SIEM/XDR Monitoring
View Category7 tools agents can invoke

DugganUSA Threat Intelligence Claude Connector FAQ
How the directory, categories and Discoverability Score work.
Read the methodologyHow do I improve DugganUSA Threat Intelligence's Claude Connector discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are DugganUSA Threat Intelligence alternatives on Claude?
As of 2026-10-28, DugganUSA Threat Intelligence competes with Anvilogic, Brandefense MCP, DarkWebSonar, ELLIO, Exaforce, Fingerprint, Have I Been Squatted, IntelMCP and 7 more in Claude Threat Detection & SIEM/XDR Monitoring, ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.